NPC confirms data breach in 10 government agencies
DICT exec: All breaches contained
MANILA, Philippines — National Privacy Commission (NPC) is evaluating data breach notifications filed by at least 10 major government agencies and institutions following a series of cybersecurity incidents.
The privacy watchdog has confirmed receiving notifications on Tuesday from key national government agencies including the Department of Information and Communications Technology (DICT), Presidential Commission on Good Government, Department of Labor and Employment’s Bureau of Local Employment, Bureau of Internal Revenue (BIR) and the Philippine Amusement and Gaming Corp.
Also submitting breach notifications were the Department of Justice Office for Alternative Dispute Resolution, Securities and Exchange Commission, Philippine Coast Guard, Department of Trade and Industry and the Department of Science and Technology-Philippine Institute of Volcanology and Seismology.
Jose Belarmino II, NPC deputy privacy commissioner and spokesman, explained that under NPC Circular No. 16-03, filing breach notifications is a mandatory regulatory step, but stressed that reporting alone does not absolve agencies of liability.
“Breach notification is only one part of an agency’s responsibility under the Data Privacy Act. Equally important is how the agency responds to the incident, protects the individuals who may be affected and addresses the vulnerabilities that may have contributed to the breach,” Belarmino said.
He added that each filing is being evaluated by the NPC’s Compliance and Monitoring Division, which will submit findings and recommendations to the commission to determine appropriate regulatory action.
The privacy body also issued a stern reminder to government offices using external contractors, reiterating that outsourcing IT or data processing services does not relieve state agencies of their legal obligations under Republic Act 10173, or the Data Privacy Act of 2012.
Citing Section 21 of the DPA, the NPC emphasized that government agencies, acting as personal information controllers, remain fully accountable for data under their custody, even if the breach occurred through third-party vendors.
“Where the prescribed conditions for mandatory notification are met, affected data subjects must also be notified in accordance with the requirements and timelines set under the Circular,” Belarmino stressed, calling on agencies to execute concrete measures to prevent recurring security lapses.
Amid the wave of reported exposures, the NPC cautioned the public to stay vigilant against potential phishing schemes, scam messages, identity theft and social engineering attacks that may exploit concern over the recent data breaches.
The NPC issued the statement in response to a report by cybersecurity monitoring watchdog Deep Web Konek recently flagging a massive wave of data breach and exposure incidents allegedly affecting as many as 23 local institutions, including major national government agencies such as government departments, including even the DICT, law enforcement agencies, military force units and educational institutions.
Based on an official intelligence assessment published by the group covering monitored underground disclosures from Nov. 5 to 7, the leaks involve millions of personal, corporate and administrative records, along with one website defacement event.
Military and uniformed services were likewise tagged in the report.
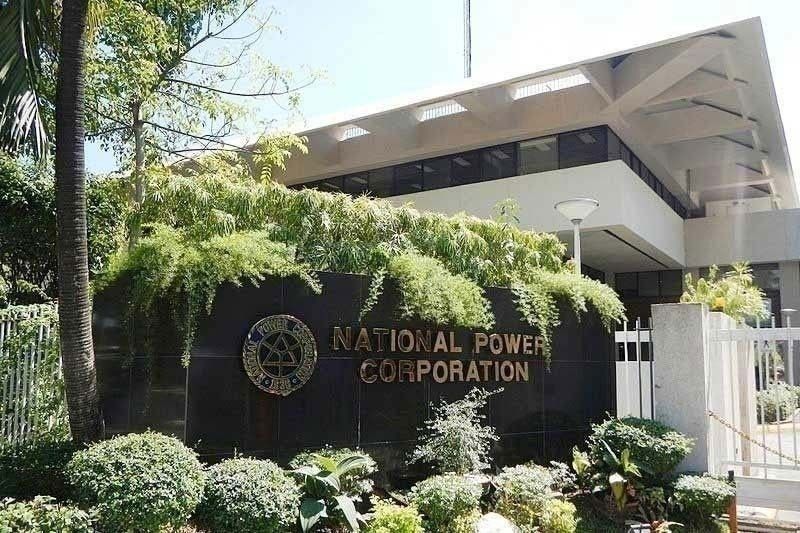
Data exposures also extended to key public utility and private logistics firms, including the National Power Corp., Mactan Electric Co., and LBC Express, which allegedly suffered a compromise involving 20.9 million customer shipment logs.
Educational institutions named in the summary include the University of Camarines Norte, Cavite State University-General Trias Campus, Nueva Ecija University of Science and Technology and the University of St. La Salle.
According to the monitoring report, the breached data categories encompass personally identifiable information, government IDs, taxpayer and corporate registration details, employee and HR records, payroll data, student files and operational logs.
BIR Data ‘exposed’
The BIR said some taxpayer profile information may have been exposed following cybersecurity incidents, but initial findings showed that filing and payment records were not compromised.
In an advisory issued on Tuesday, the BIR said it is “actively responding” to incidents reported on Nov. 6 and 7, prompting the agency to take immediate steps to preserve evidence, prevent further exposure and determine the extent of affected records.
“The BIR assures the public that the integrity of all internal database infrastructure and systems remain intact. Initial findings indicate that no taxpayer information was modified or lost and no records on filing and payment were compromised,” it said.
However, the agency said findings “indicate that certain taxpayer profile information may have been exposed.”
The BIR, in coordination with the Cybercrime Investigation and Coordinating Center and the DICT- National Computer Emergency Response Team, is conducting a forensic investigation to verify the source and extent of any unauthorized access.
The NPC has also been notified in accordance with existing laws, rules and regulations, according to the tax agency.
“The BIR recognizes the concerns arising from these incidents and assures the public it is taking measures to protect taxpayer information. To fully address system vulnerability, the BIR is strengthening access controls and testing all remediation measures,” it said.
With this, the BIR urged taxpayers to update their account credentials, enable multi-factor authentication, regularly monitor account activity and remain vigilant against phishing attempts and other fraudulent communications.
Taxpayers were advised to conduct transactions exclusively through the BIR’s official channels and platforms. – Aubrey Rose Inosante


- Latest
- Trending